Creators of Apache Ranger Launched AI Agent Security Guide Series for CISOs
Creators of Apache Ranger launched an agent security guide that provides practical criteria for evaluating security

Press Release Disclaimer: This is a press release distributed through the XPR Media network. It has not been independently verified by our newsroom.
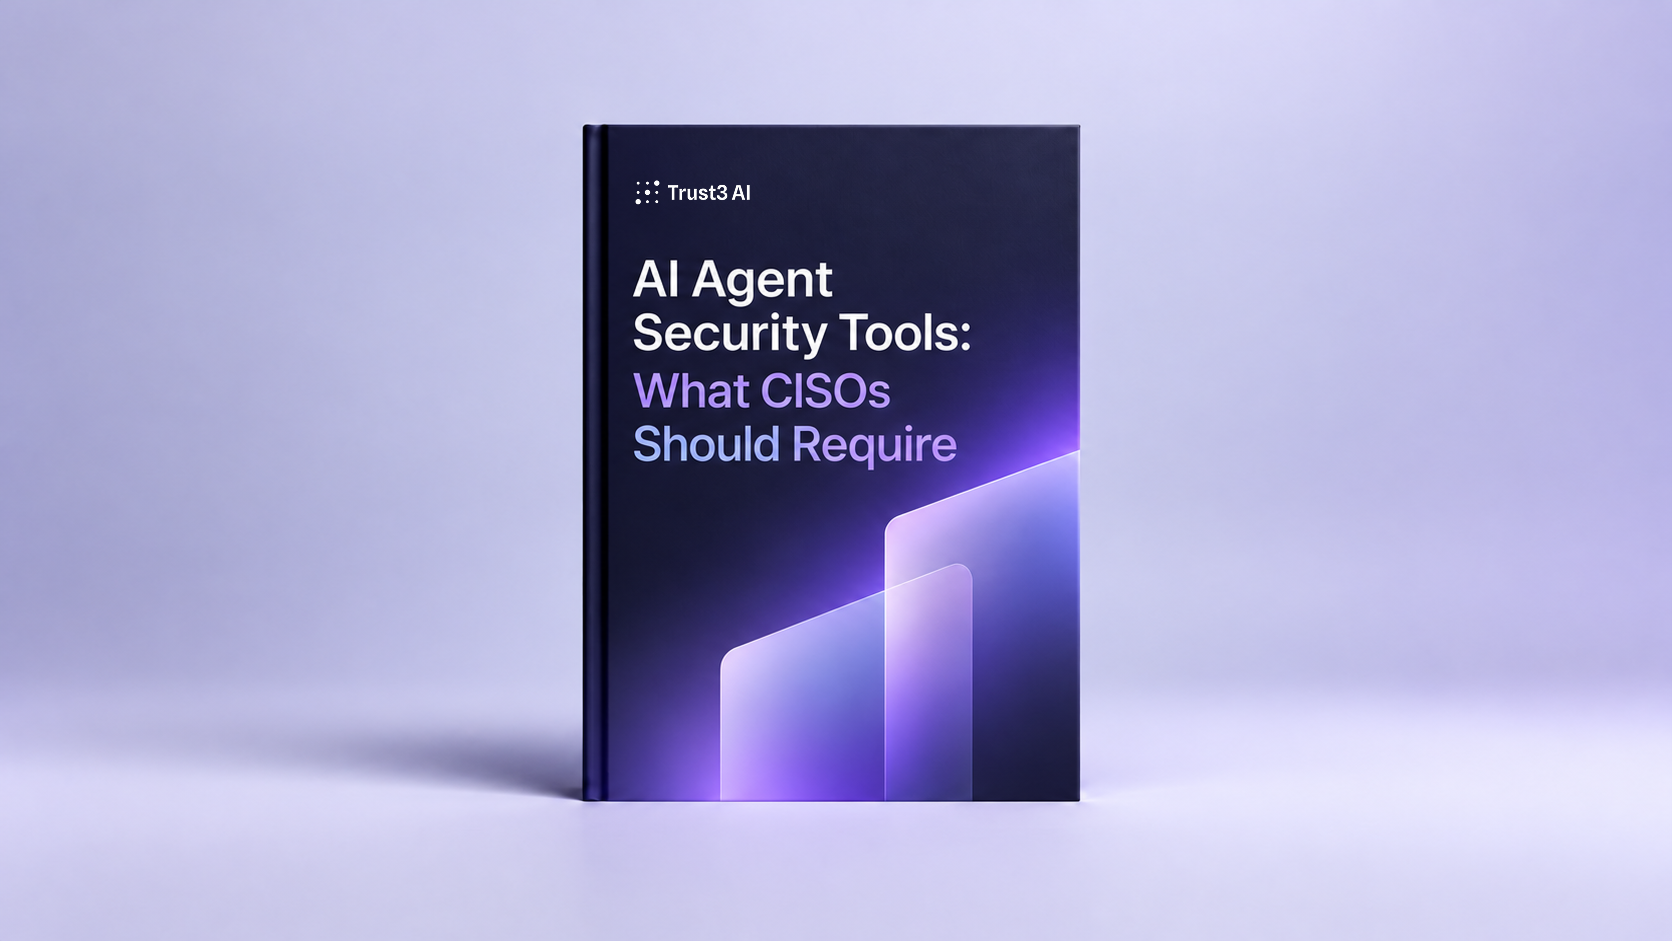

Creators of Apache Ranger launched an agent security guide that provides practical criteria for evaluating security tools across the agent lifecycle.
SAN FRANCISCO, CA, UNITED STATES, October 15, 2026 /EINPresswire.com/ — Trust3 AI, founded by the creators of Apache Ranger, today announced a technical guide series to help CISOs evaluate AI agent security tools. The first chapter, “AI Agent Security Tools: What CISOs Should Require,” examines four security categories, their capabilities, and the gaps enterprises should address before deploying agents in production.
AI agents call tools, connect to Model Context Protocol (MCP) servers, execute code, and access enterprise data on behalf of users. Securing those agents requires controls over their actions, identities, and permissions, alongside protections for prompts and responses.
The guide helps CISOs, security teams, and data and agent practitioners assess how different tools work together across development and runtime. Chapter 1 examines:
– Adversarial testing: Identifying weaknesses before deployment.
– Tool and MCP scanning: Detecting poisoned tools and unsafe configurations.
– Runtime isolation: Containing the code agents execute.
– Agent security control planes: Discovering agents, tracing activity, and enforcing authorization through supported integrations.
The chapter provides evaluation criteria covering integration coverage, agent registration, continuous testing, identity propagation, runtime authorization, audit trails, and access enforcement at the data source. It also explains why agent security is incomplete without data security.
“Apache Ranger helped enterprises control who could access their data. AI agents make that question more complex: which agent is acting, on whose behalf, and what is it authorized to do?” said Don Bosco Durai, Co-Founder and CTO of Trust3 AI. “This series helps CISOs evaluate those controls before agents reach production.”
Chapter 1 is available at trust3.ai/ai-agent-security-tools. Additional chapters will follow.
ABOUT TRUST3 AI
Trust3 AI is the security control plane for enterprise AI agents and data. The platform applies purpose-based access control across agent actions and the data agents reach, from build time to runtime. Trust3 AI connects to any agentic framework and governs agents across clouds, platforms, and AI gateways including Databricks, Microsoft, and Snowflake environments. Enterprises use it to discover every agent, observe every decision, and secure every action. Trust3 AI is a Databricks Built On Partner, a member of the NVIDIA Inception program, and a member of the Snowflake Startup Accelerator.
Learn more at trust3.ai or request a demo at trust3.ai/demo.
Media Contact
Angela Chen
angela@trust3.ai
Angela Chen
Trust3 AI
angela@trust3.ai
Visit us on social media:
LinkedIn
Instagram
YouTube
X
Legal Disclaimer:
EIN Presswire provides this news content “as is” without warranty of any kind. We do not accept any responsibility or liability
for the accuracy, content, images, videos, licenses, completeness, legality, or reliability of the information contained in this
article. If you have any complaints or copyright issues related to this article, kindly contact the author above.

Media gallery